基于角色的访问控制(RBAC)
🌐 Role-Based Access Control (RBAC)
Page summary:基于角色的访问控制(RBAC)管理管理员角色和管理面板中的细粒度权限。本文件涵盖创建角色、分配权限以及保护管理工作流程。
基于角色的访问控制(RBAC)功能允许管理管理员,即管理面板的用户。更具体地说,RBAC 管理管理员的账户和角色。
🌐 The Role-Based Access Control (RBAC) feature allows the management of the administrators, who are the users of the admin panel. More specifically, RBAC manages the administrators' accounts and roles.
配置
🌐 Configuration
配置此功能的路径: 设置 > 管理面板 > 角色
角色界面显示了为你的 Strapi 应用的管理员创建的所有角色。
🌐 The Roles interface displays all created roles for the administrators of your Strapi application.
通过该界面,可以:
🌐 From this interface, it is possible to:
默认情况下,为任何 Strapi 应用定义了 3 个管理员角色:
🌐 By default, 3 administrator roles are defined for any Strapi application:
- 作者:能够创建和管理自己的内容。
- 编辑:能够创建内容,管理和发布任何内容。
- 超级管理员:能够访问所有功能和设置。这是 Strapi 应用创建时默认分配给第一个管理员的角色。
创建新角色
🌐 Creating a new role
在 管理面板 > 角色 界面的右上角,会显示一个 添加新角色 按钮。点击该 添加新角色 按钮,为你的 Strapi 应用的管理员创建一个新角色。
🌐 On the top right side of the Administration panel > Roles interface, an Add new role button is displayed. Click on that Add new role button to create a new role for administrators of your Strapi application.
你将被重定向到角色编辑界面,在那里你可以编辑角色的详细信息并配置其权限(参见编辑角色)。
🌐 You will be redirected to the roles edition interface, where you will be able to edit the role's details and configure its permissions (see Editing a role).
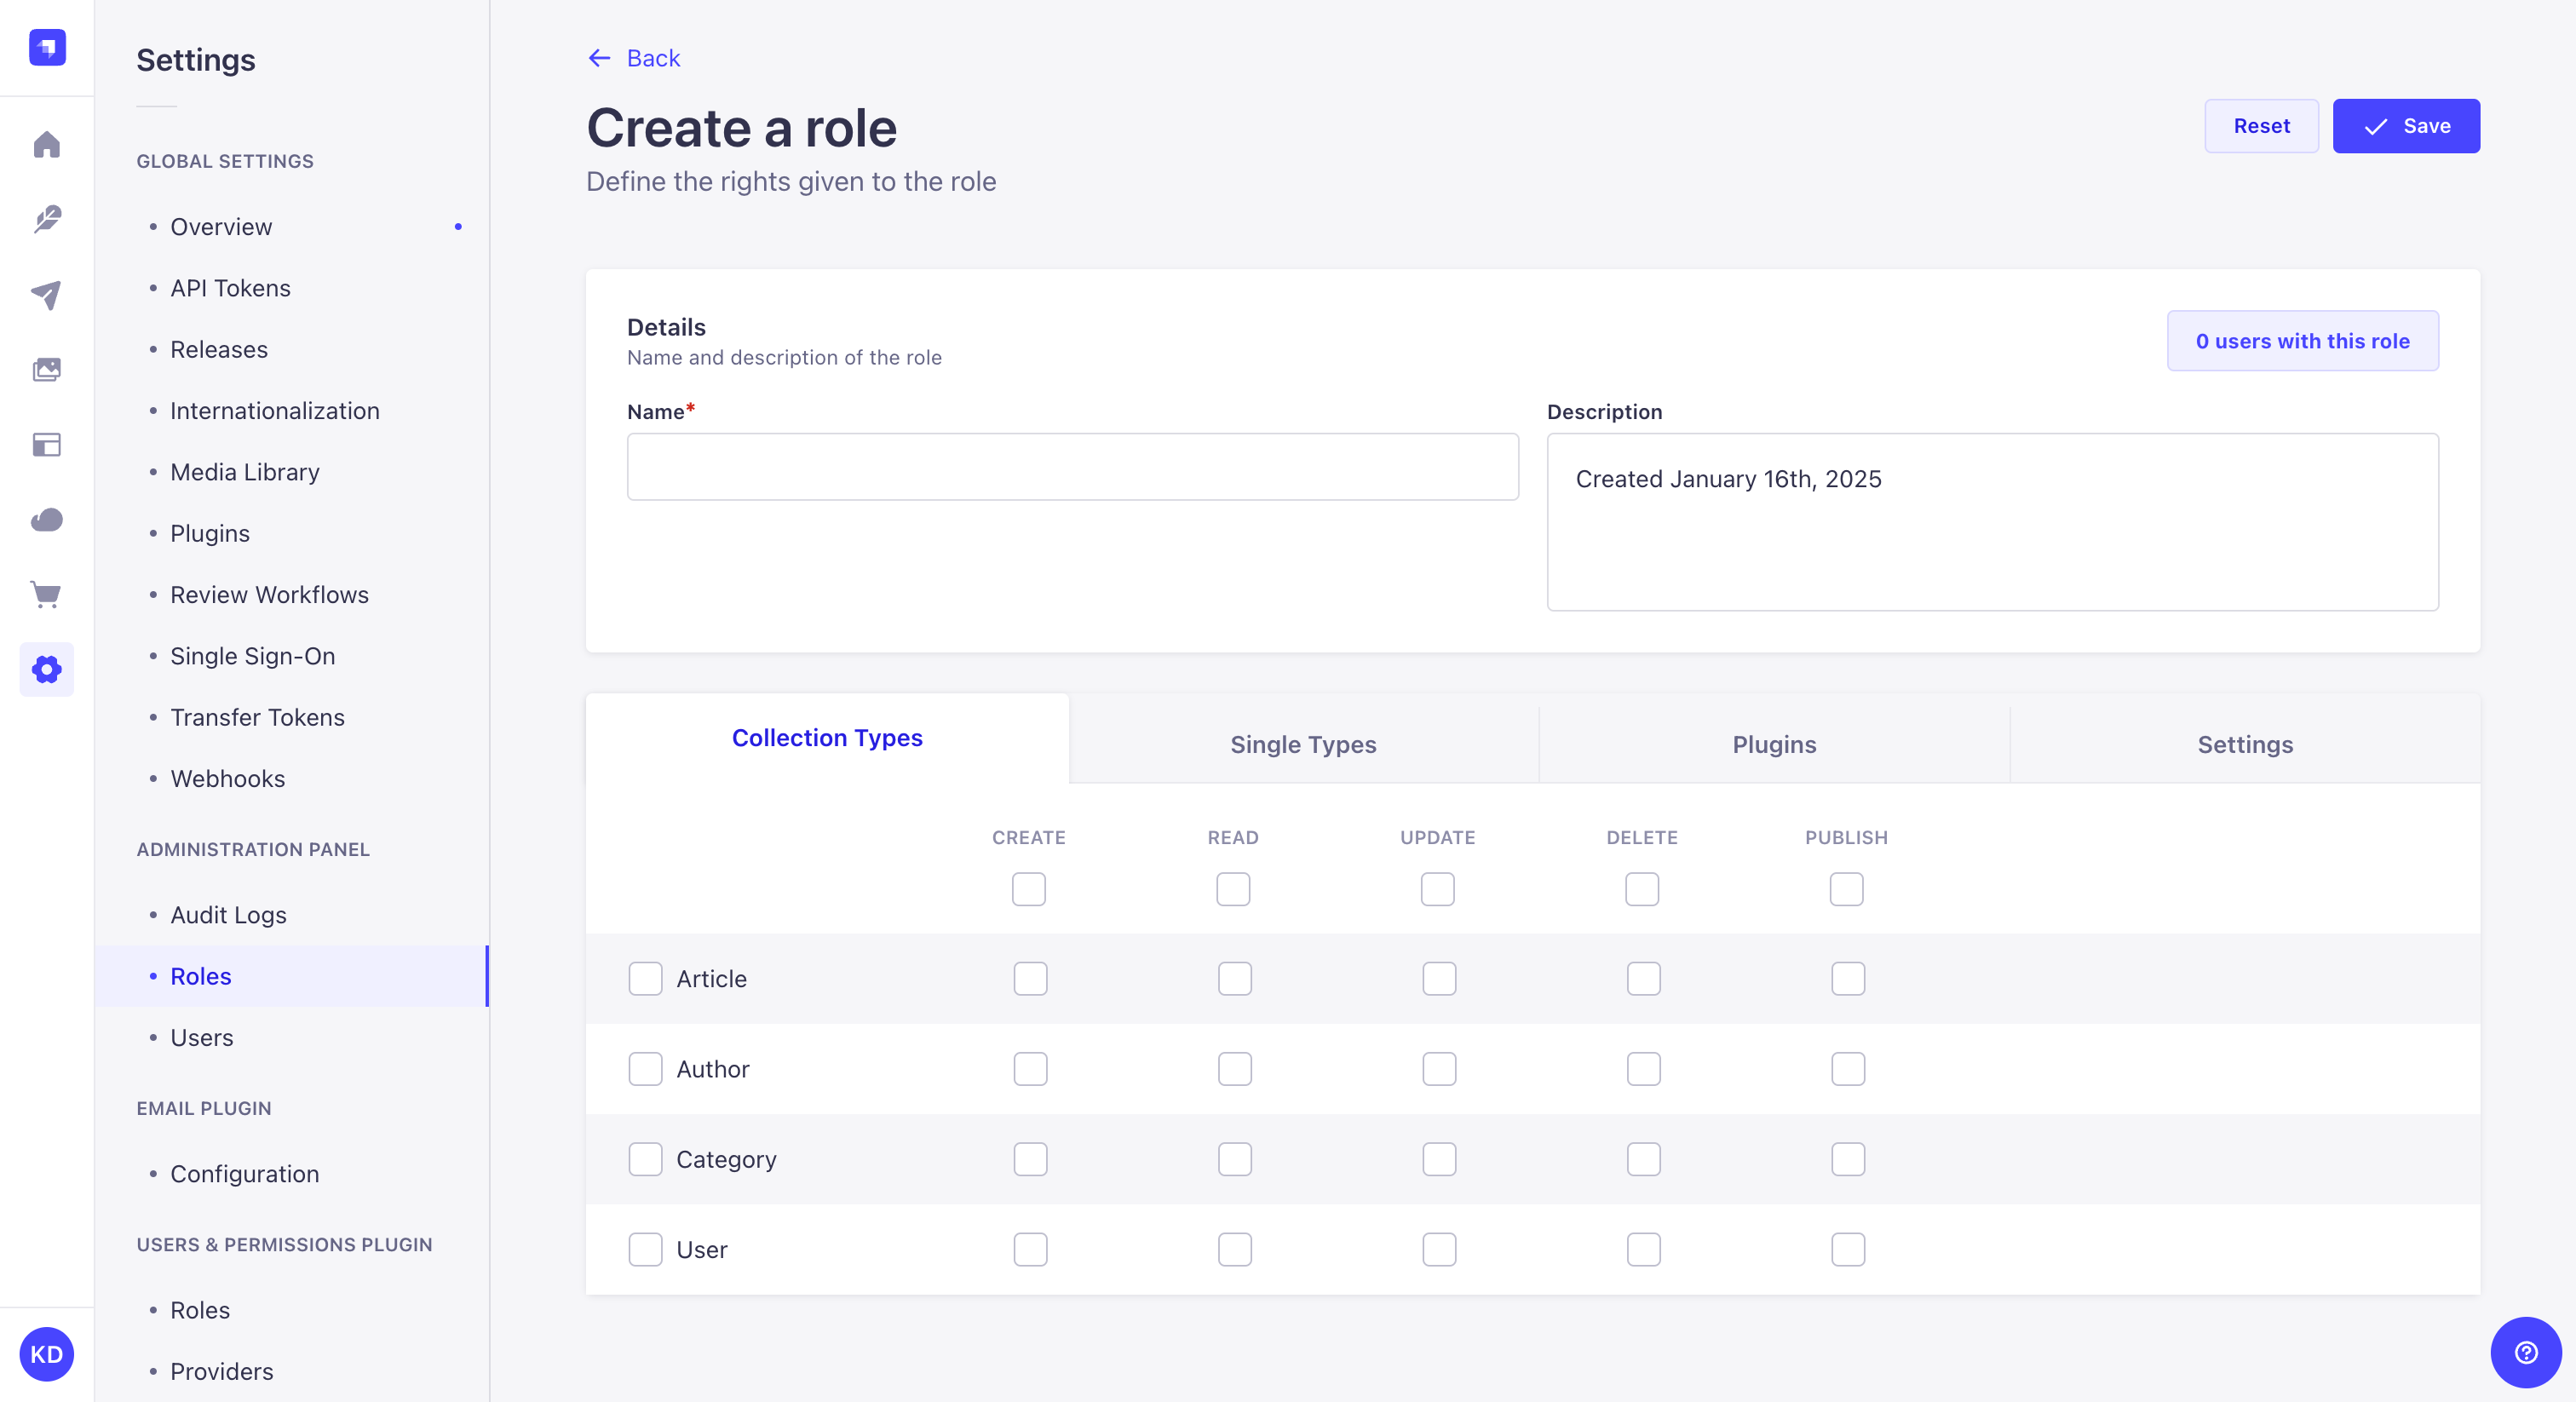
在 Roles 界面中,你可以从表格点击重复按钮 通过复制现有角色来创建新角色。
删除角色
🌐 Deleting a role
管理员角色可以从 管理面板 > 角色 界面中删除。然而,只有在它们不再被分配给任何 Strapi 应用的管理员时,才能删除。
🌐 Administrator roles can be deleted from the Administration panel > Roles interface. However, they can only be deleted once they are no more attributed to any administrator of the Strapi application.
- 确保你要删除的角色不再归属于任何管理员。
- 点击角色记录右侧的删除按钮 。
- 在删除窗口中,点击 确认 按钮以确认删除。
编辑角色
🌐 Editing a role
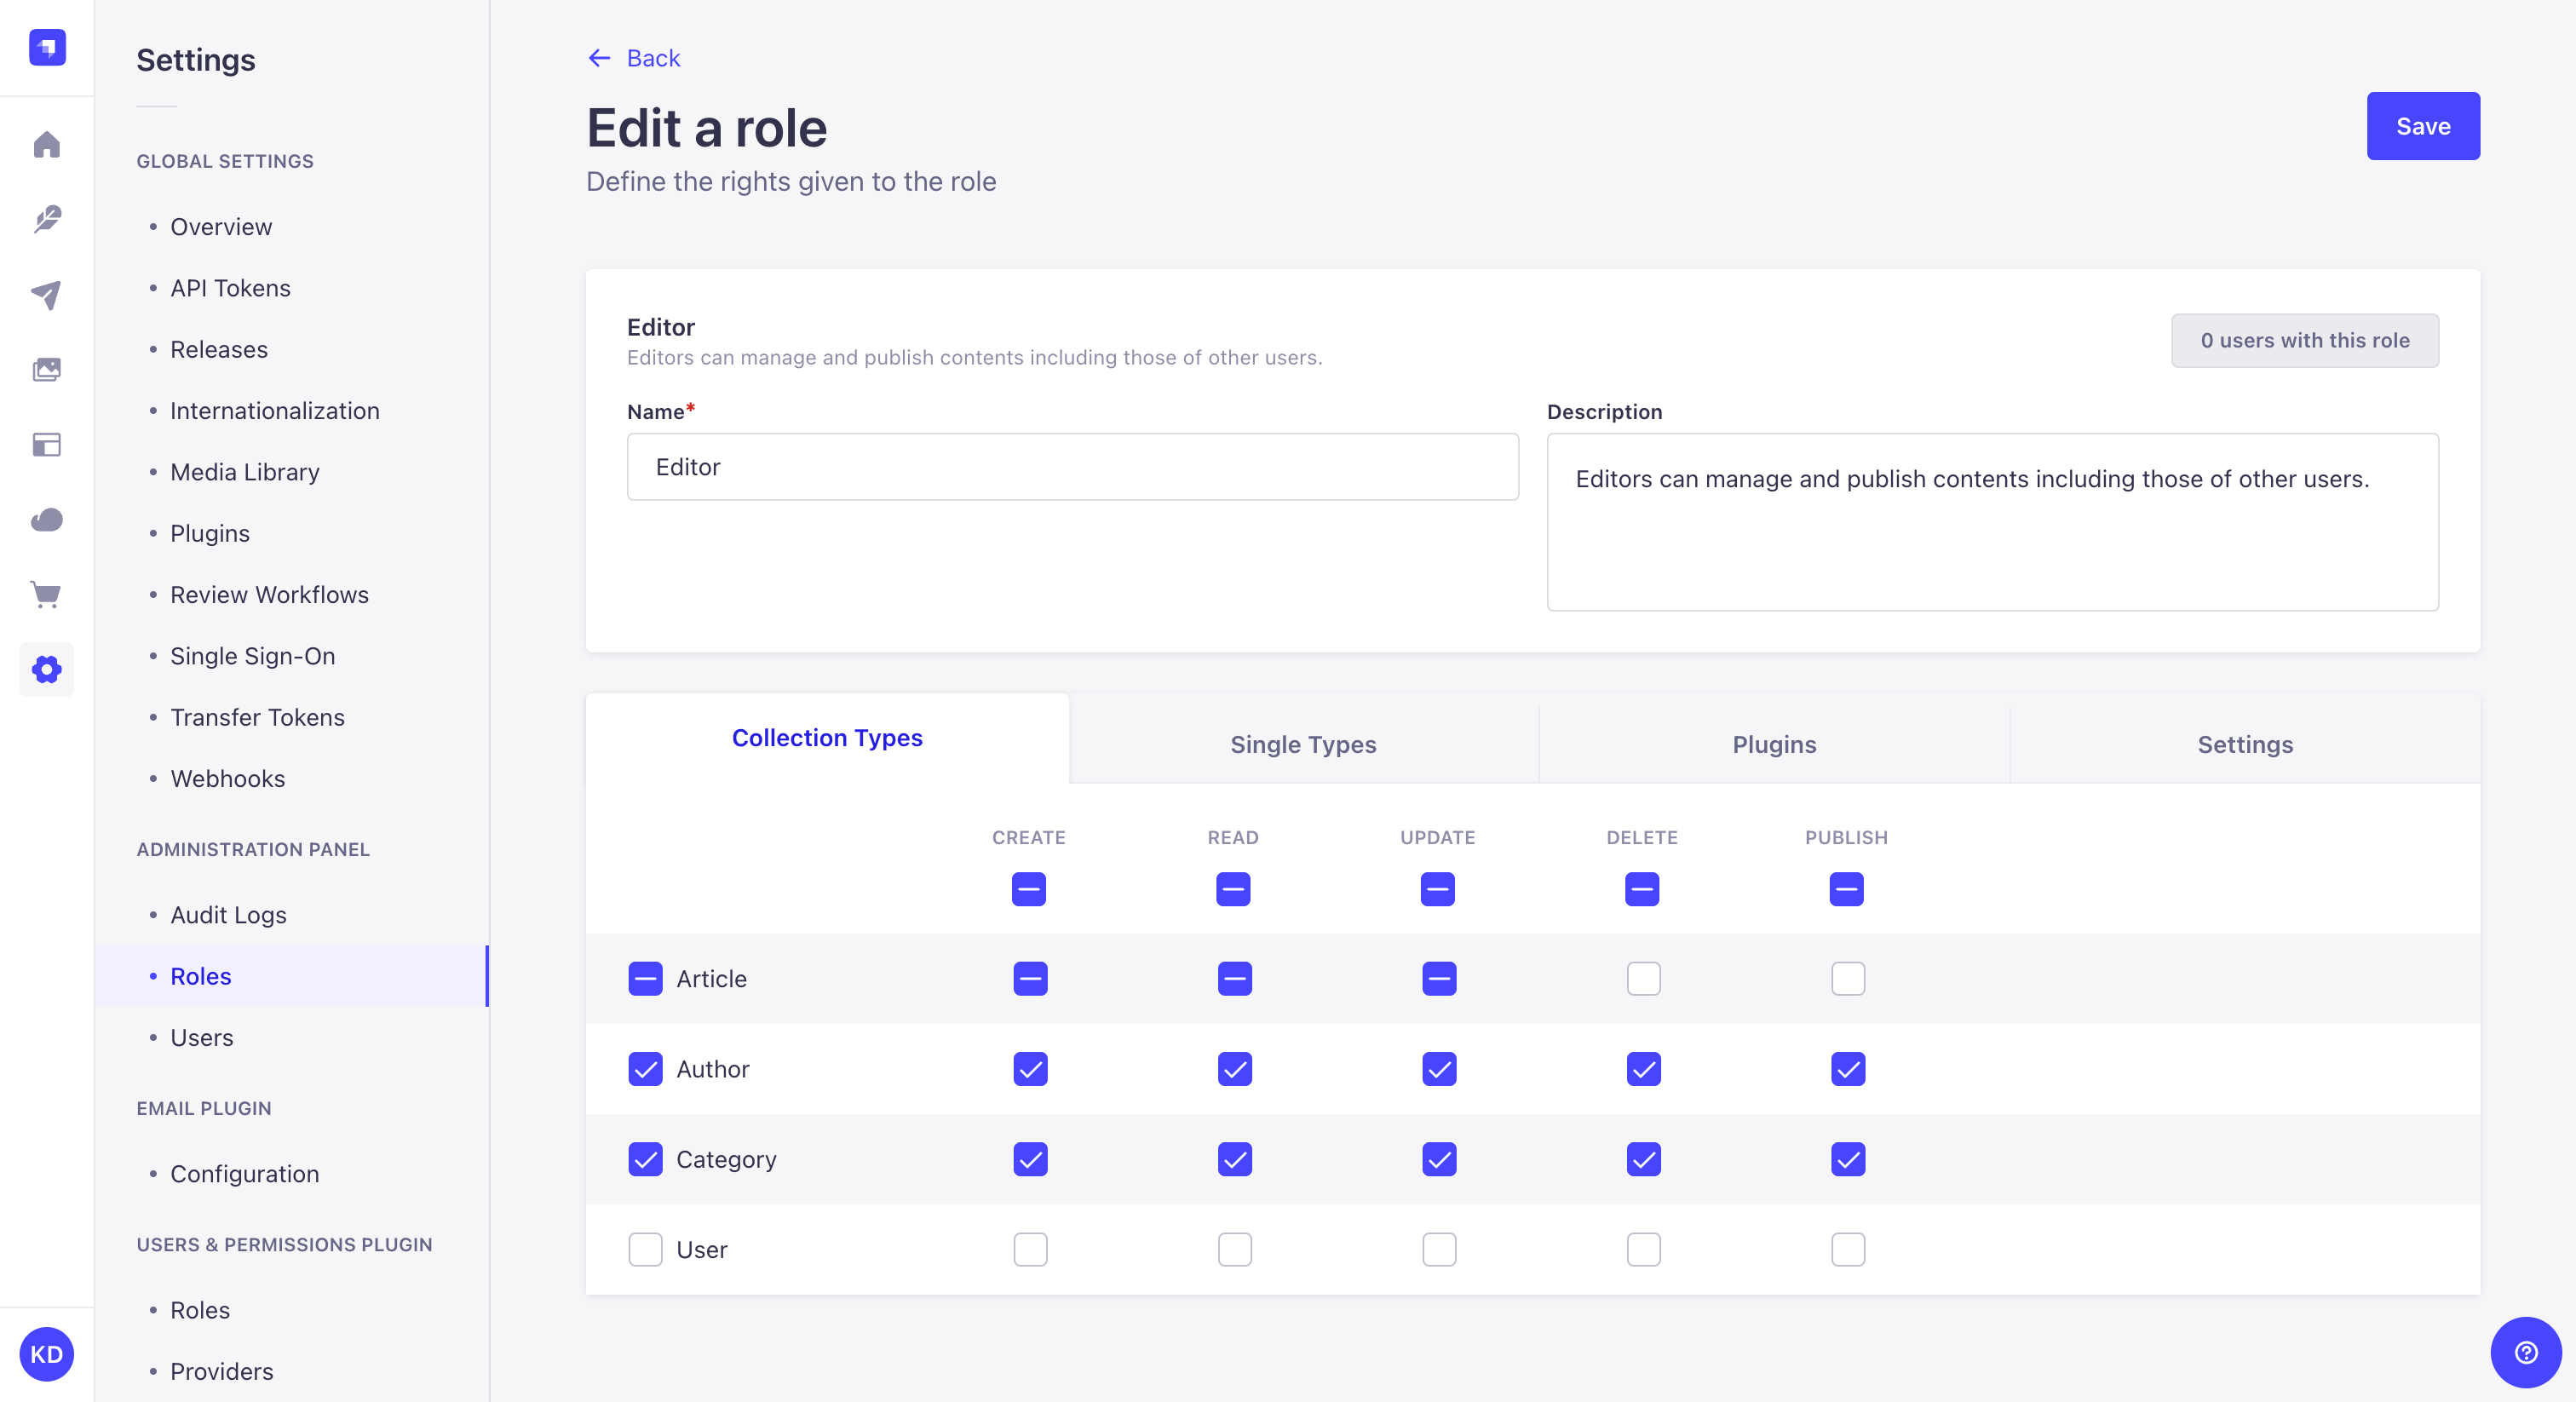
角色编辑界面允许你编辑管理员角色的详细信息,并且可以详细配置你 Strapi 应用的各个部分的权限。
🌐 The role edition interface allows you to edit the details of an administrator role as well as configure in detail the permissions to all sections of your Strapi application.
可以通过 管理面板 > 角色 访问,方法是在角色记录右侧点击编辑按钮 ,或者点击 添加新角色 按钮(参见 创建新角色)。
无法编辑超级管理员角色的权限。所有配置都是只读模式。
🌐 It isn't possible to edit the permissions of the Super Admin role. All configurations are in read-only mode.
编辑角色的详情
🌐 Editing role's details
管理员角色编辑界面的详细信息区域允许你定义角色的名称,并为其提供一个描述,这有助于其他管理员理解该角色可以访问什么内容。
🌐 The details area of an administrator role editing interface allows you to define the name of the role, and to give it a description that should help other administrators understand what the role gives access to.
| 角色详情 | 说明 |
|---|---|
| 名称 | 在文本框中输入角色的新名称。 |
| 描述 | 在文本框中输入角色的描述。 |
在右上角,你可以看到一个计数器,指示有多少管理员被赋予了该角色。
🌐 In the top right corner, you can see a counter indicating how many administrators have been attributed the role.
配置角色权限
🌐 Configuring role's permissions
管理员角色编辑界面的权限区域允许你详细配置管理员可以在 Strapi 应用的任何部分执行哪些操作。
🌐 The permissions area of an administrator role editing interface allows you to configure in detail what actions an administrator can do for any part of the Strapi application.
它显示为一个表格,分为4类:集合类型、单一类型、插件和设置。
🌐 It is displayed as a table, split into 4 categories: Collection types, Single types, Plugins and Settings.
集合类型和单一类型
🌐 Collection and Single types
集合类型和单一类型类别分别列出了 Strapi 应用的所有可用集合和单一类型。
🌐 The Collection types and Single types categories respectively list all available collection and single types for the Strapi application.
对于每种内容类型,管理员可以拥有执行以下操作的权限:创建、读取、更新、删除和发布。
🌐 For each content-type, the administrators can have the permission to perform the following actions: create, read, update, delete and publish.
- 转到权限表的集合类型或单一类型类别。
- 勾选内容类型名称左侧的框以授予访问权限。默认情况下,所有操作都可以在内容类型的所有字段上执行。
- (可选)取消选中与操作相关的框,以防止你选择的操作。
- (可选) 点击内容类型的名称以显示其完整字段列表。取消选中字段和操作相关的选框,以防止对所选字段的访问和/或操作。如果已安装国际化功能,还要定义应为每个可用语言设置的权限。
- 对角色应授予访问权限的每个可用内容类型重复步骤 2 至 4。
- 点击右上角的保存按钮。
插件和设置
🌐 Plugins and Settings
插件和设置类别都显示 Strapi 应用中每个可用插件或设置的子类别。每个子类别都包含其特定的权限集合。
🌐 The Plugins and Settings categories both display a sub-category per available plugin or setting of the Strapi application. Each sub-category contains its own specific set of permissions.
- 转到权限表的插件或设置类别。
- 单击要配置权限的子类别名称,可显示所有可用权限。
- 勾选该角色应授予访问权限的选项。你可以参考下表以获取更多信息和说明。
- Plugins
- Settings
默认情况下,包的权限可以为 内容类型生成器、上传(即媒体库)、内容管理器 和 用户与权限(即允许你管理终端用户的用户与权限功能)进行配置。每个包都有自己特定的权限集合。
🌐 By default, packages permissions can be configured for the Content-type Builder, Upload (i.e. Media Library), the Content Manager, and Users & Permissions (i.e. the Users & Permissions feature allowing you to manage end users). Each package has its own specific set of permissions.
| 包名 | 权限 |
|---|---|
| 内容发布 (发布) |
|
| 内容管理器 |
|
| 内容类型构建器 |
|
| 上传 (媒体库) |
|
| 用户-权限 |
常规 > 设置 > 用户与权限插件 |
可以为从管理员面板主导航的 常规 > 设置 访问的所有设置配置权限。它们还允许你配置对管理员面板中插件和市场部分的访问。每个设置都有自己特定的权限集合。
🌐 Settings permissions can be configured for all settings accessible from General > Settings from the main navigation of the admin panel. They also allow you to configure access to the Plugins and Marketplace sections of the admin panel. Each setting has its own specific set of permissions.
| 设置名称 | 权限 |
|---|---|
| 内容发布 |
常规 > 设置 > 全局设置 - 发布 |
| 电子邮件 |
常规 > 设置 > 用户与权限插件 - 电子邮件模板 |
| 媒体库 |
常规 > 设置 > 全局设置 - 媒体库 |
| 国际化 |
常规 > 设置 > 全局设置 - 国际化 |
| 审核工作流 |
常规 > 设置 > 全局设置 - 审核工作流 |
| 单点登录 |
常规 > 设置 > 全局设置 - 单点登录 |
| 审计日志 |
常规 > 设置 > 管理面板 - 审计日志 |
| 插件和市场 |
|
| Webhooks |
常规 > 设置 > 全局设置 - Webhook |
| 用户和角色 |
常规 > 设置 > 管理面板 |
| API 令牌 |
通用 > 设置 > 全局设置 - API 令牌 |
| 管理令牌 |
常规 > 设置 > 管理面板 - 管理令牌 |
| 项目 |
|
| 传输令牌 |
通用 > 设置 > 全局设置 - 传输令牌 |
- 点击右上角的保存按钮。
要为你的自定义插件创建管理员权限,请参考我们的专用指南。
🌐 To create admin permissions for your custom plugin, please refer to our dedicated guide.
为权限设置自定义条件
🌐 Setting custom conditions for permissions
在每个类别的每个权限旁边,都会显示一个 设置按钮。它允许你通过为管理员定义额外的条件来进一步配置权限。
有 2 个默认附加条件:
🌐 There are 2 default additional conditions:
- 管理员必须是创建者,
- 管理员必须具有与创建者相同的角色。
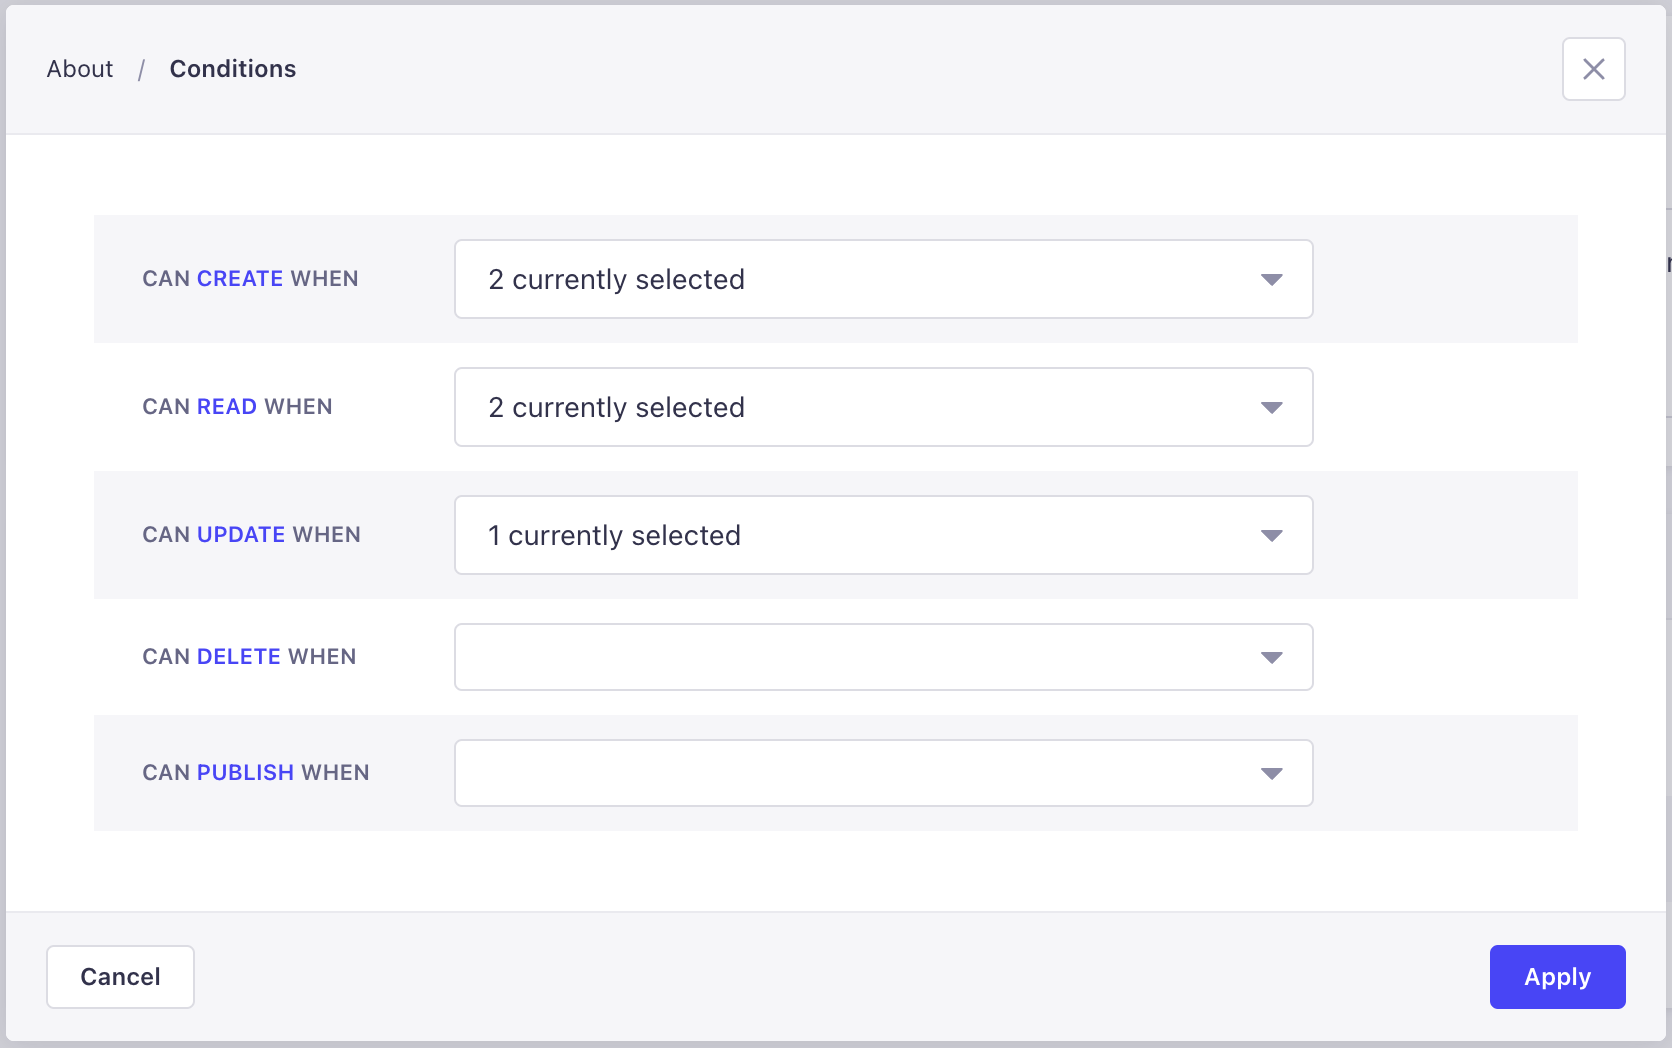
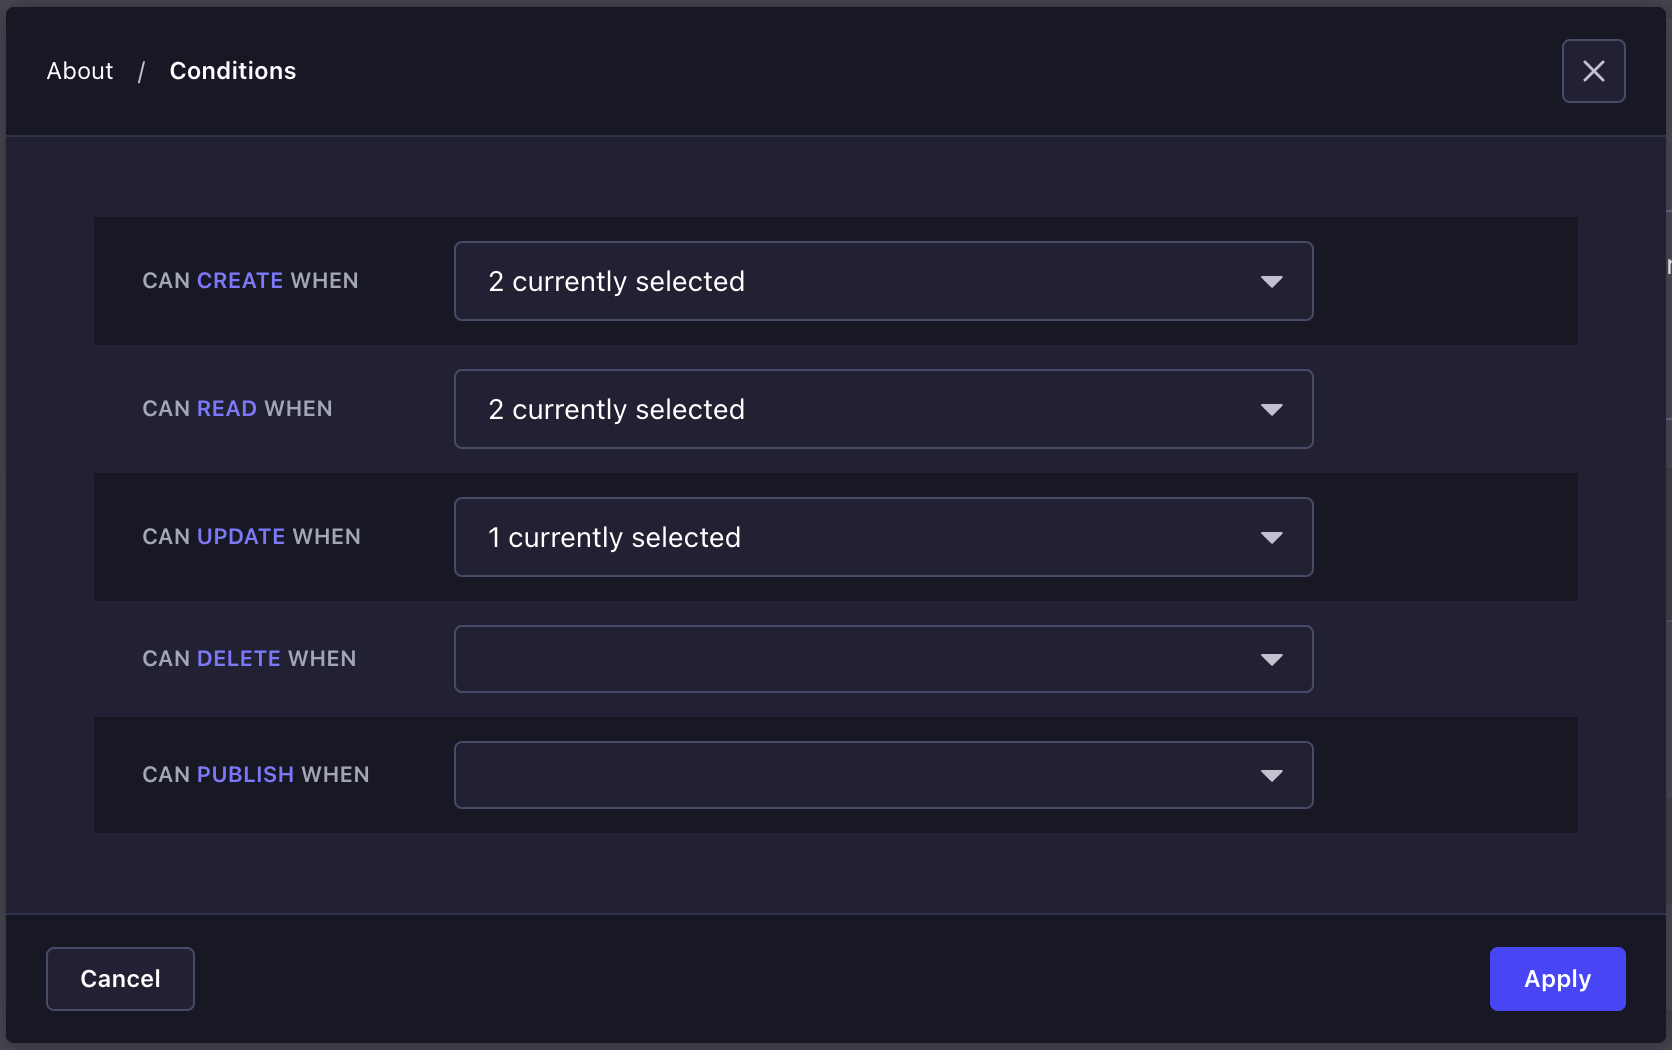
- 点击该角色已授予权限的 设置按钮。
- 在 定义条件 窗口中,每个可用权限都可以使用特定条件进行自定义。点击与要自定义的权限相关的下拉列表。
- 为所选权限定义自定义条件。你可以选择以下操作之一:
- 勾选默认选项以应用所有可用的附加条件。
- 点击箭头按钮 以查看可用的附加条件,并只勾选所选的条件。
- 点击 应用 按钮。
一旦为某个权限设置了自定义条件,就会在权限名称旁边显示一个点,以及 设置按钮。
自定义条件只能为已勾选要授予角色的权限设置。如果没有勾选,当点击 设置按钮时,打开的窗口将保持为空,因为没有可用的自定义条件选项。
如果之前已经为你的 Strapi 应用创建了,它们可以提供其他自定义条件。以下专用指南可以帮助你创建额外的自定义条件:
🌐 Other custom conditions can be available if they have been created beforehand for your Strapi application. The following dedicated guide helps you create additional custom conditions:
使用
🌐 Usage
使用此功能的路径: 设置 > 管理面板 > 用户
用户界面显示一个表格,列出你 Strapi 应用的所有管理员。更具体地说,对于表格中列出的每个管理员,其主要账户信息都会显示,包括名称、电子邮件和分配的角色。账户状态也会被指示:激活或未激活,这取决于管理员是否已经登录以激活账户。
🌐 The Users interface displays a table listing all the administrators of your Strapi application. More specifically, for each administrator listed in the table, their main account information are displayed, including name, email and attributed role. The status of their account is also indicated: active or inactive, depending on whether the administrator has already logged in to activate the account or not.
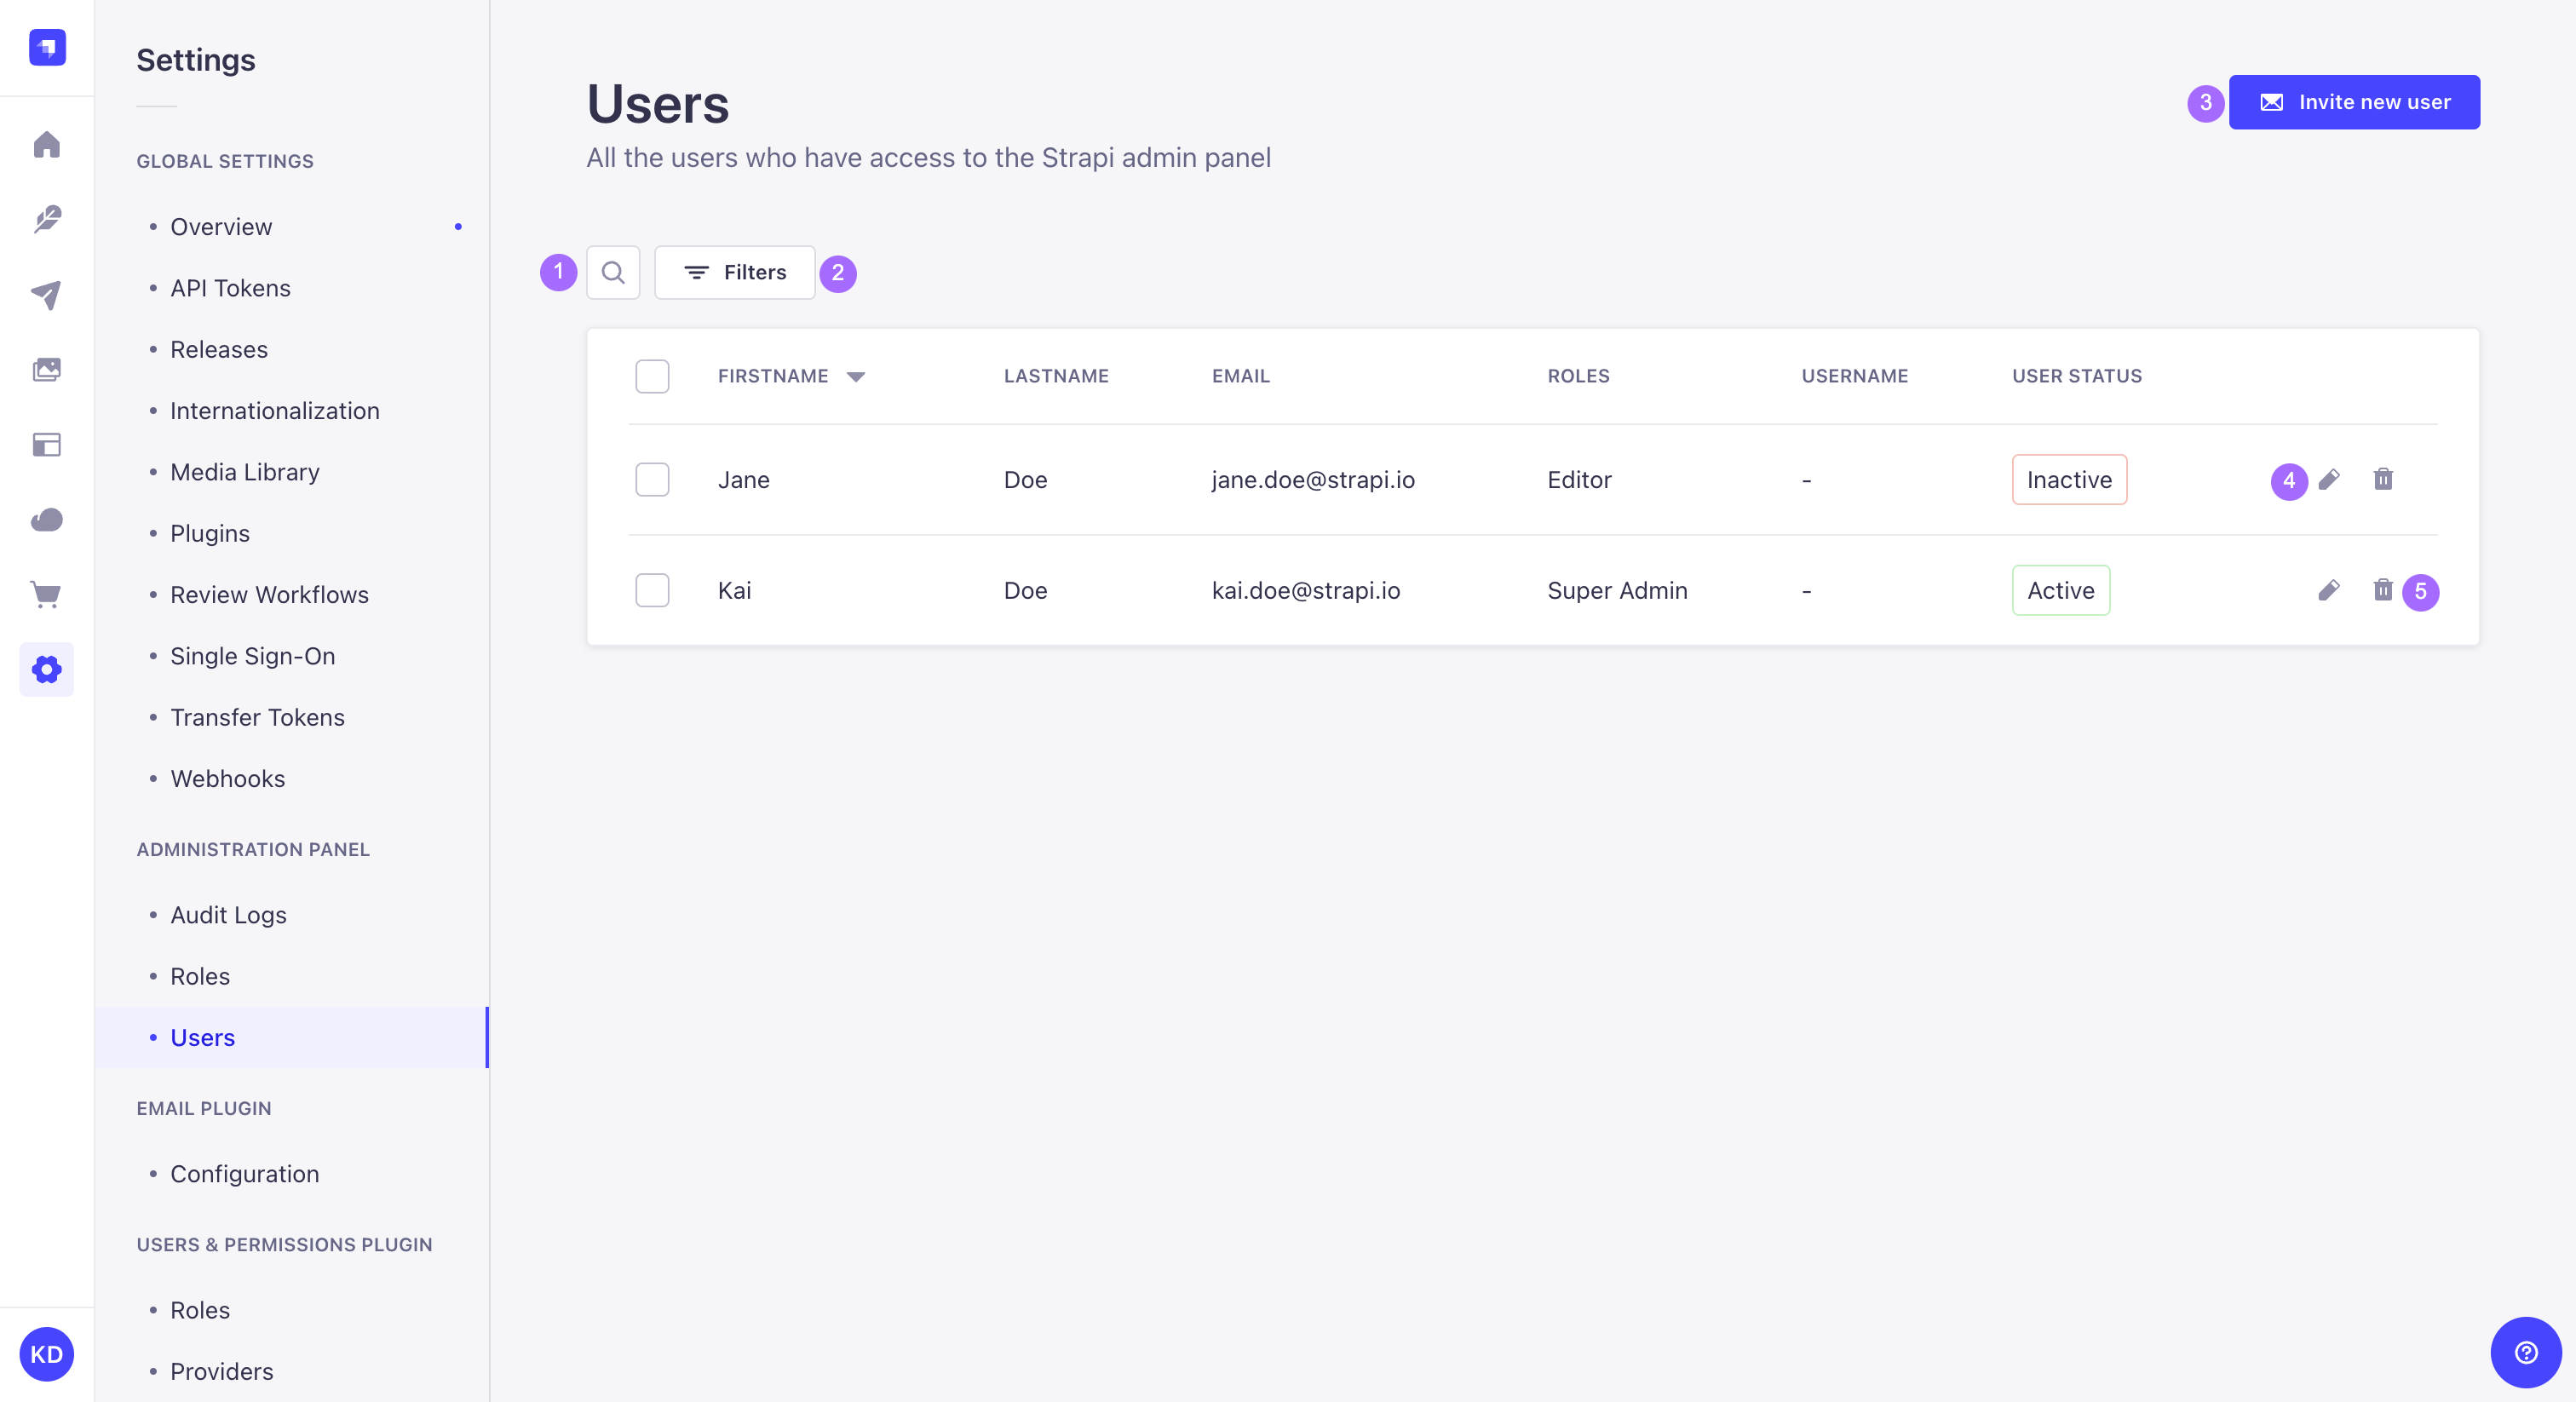
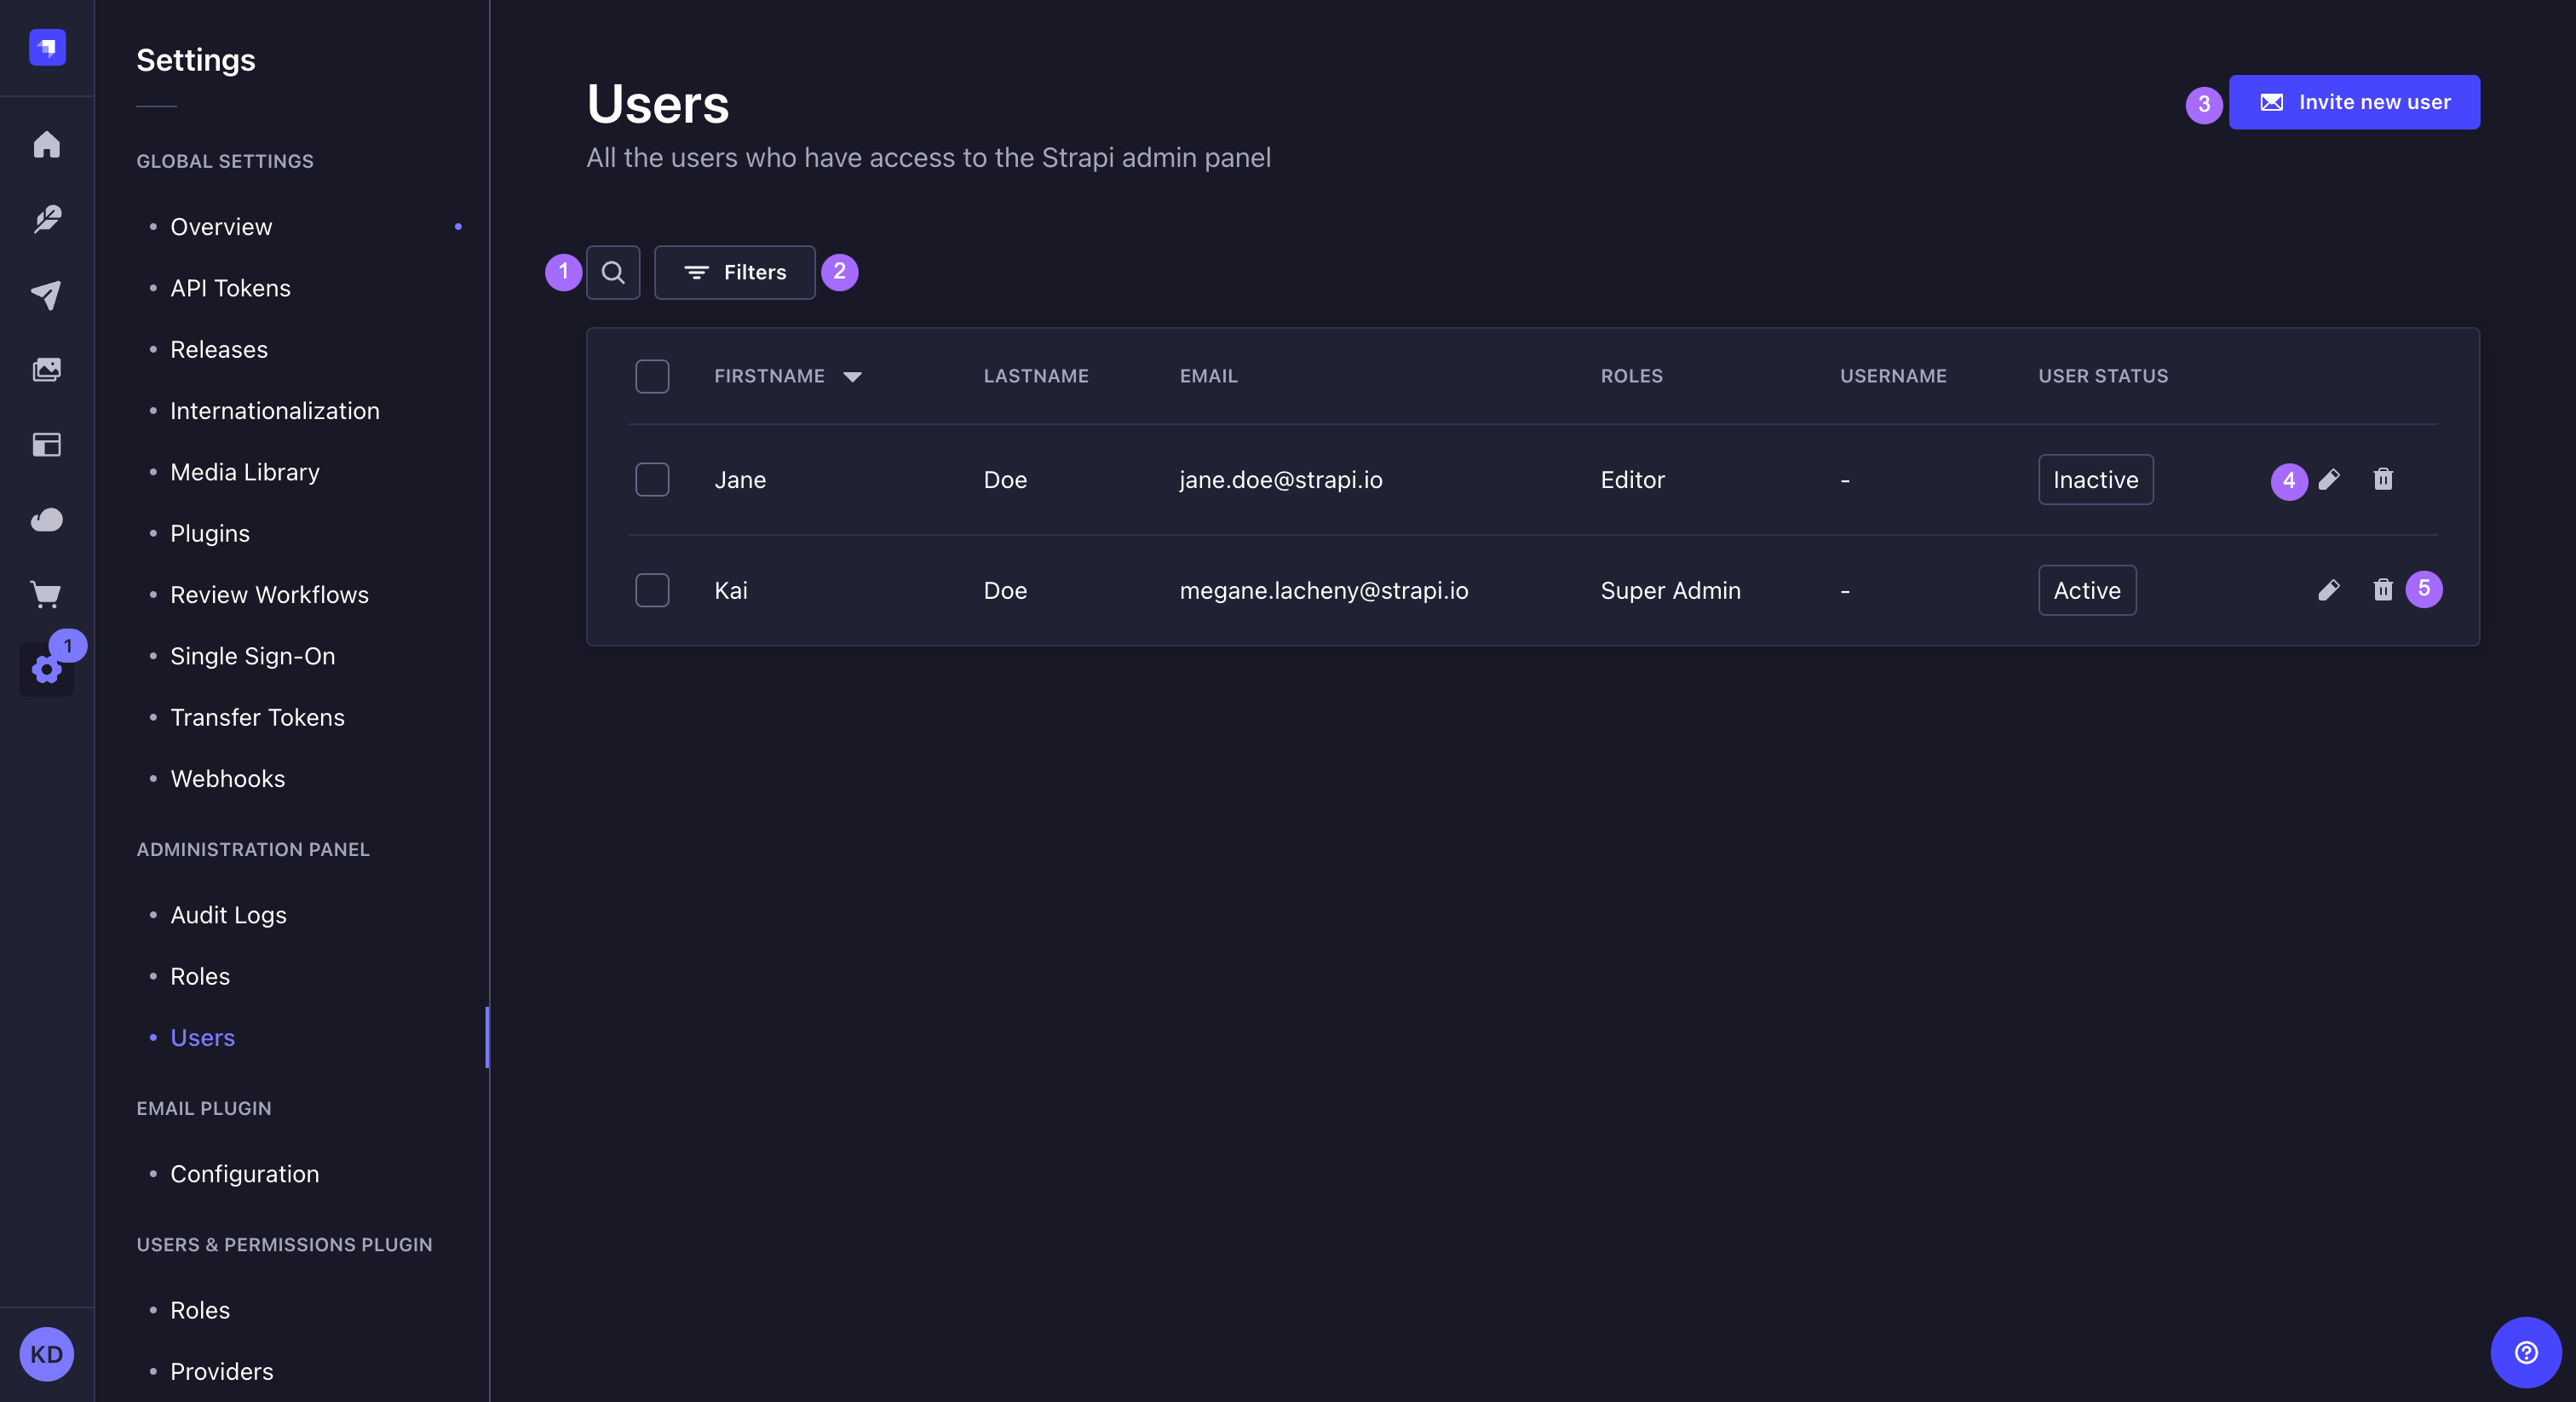
通过该界面,可以:
🌐 From this interface, it is possible to:
- 进行文本搜索 1 以查找特定的管理员,
- 设置筛选器 2 以查找特定管理员,
- 创建一个新的管理员账户(参见 创建新账户) 3,
- 删除管理员账户 4 (参见删除账户),
- 或访问有关管理员账户的信息,并编辑它 5 (参见编辑账户)。
表中显示的大多数字段都可以启用排序。点击表头中的字段名称,即可对该字段进行排序。
🌐 Sorting can be enabled for most fields displayed in the table. Click on a field name, in the header of the table, to sort on that field.
创建新账户
🌐 Creating a new account
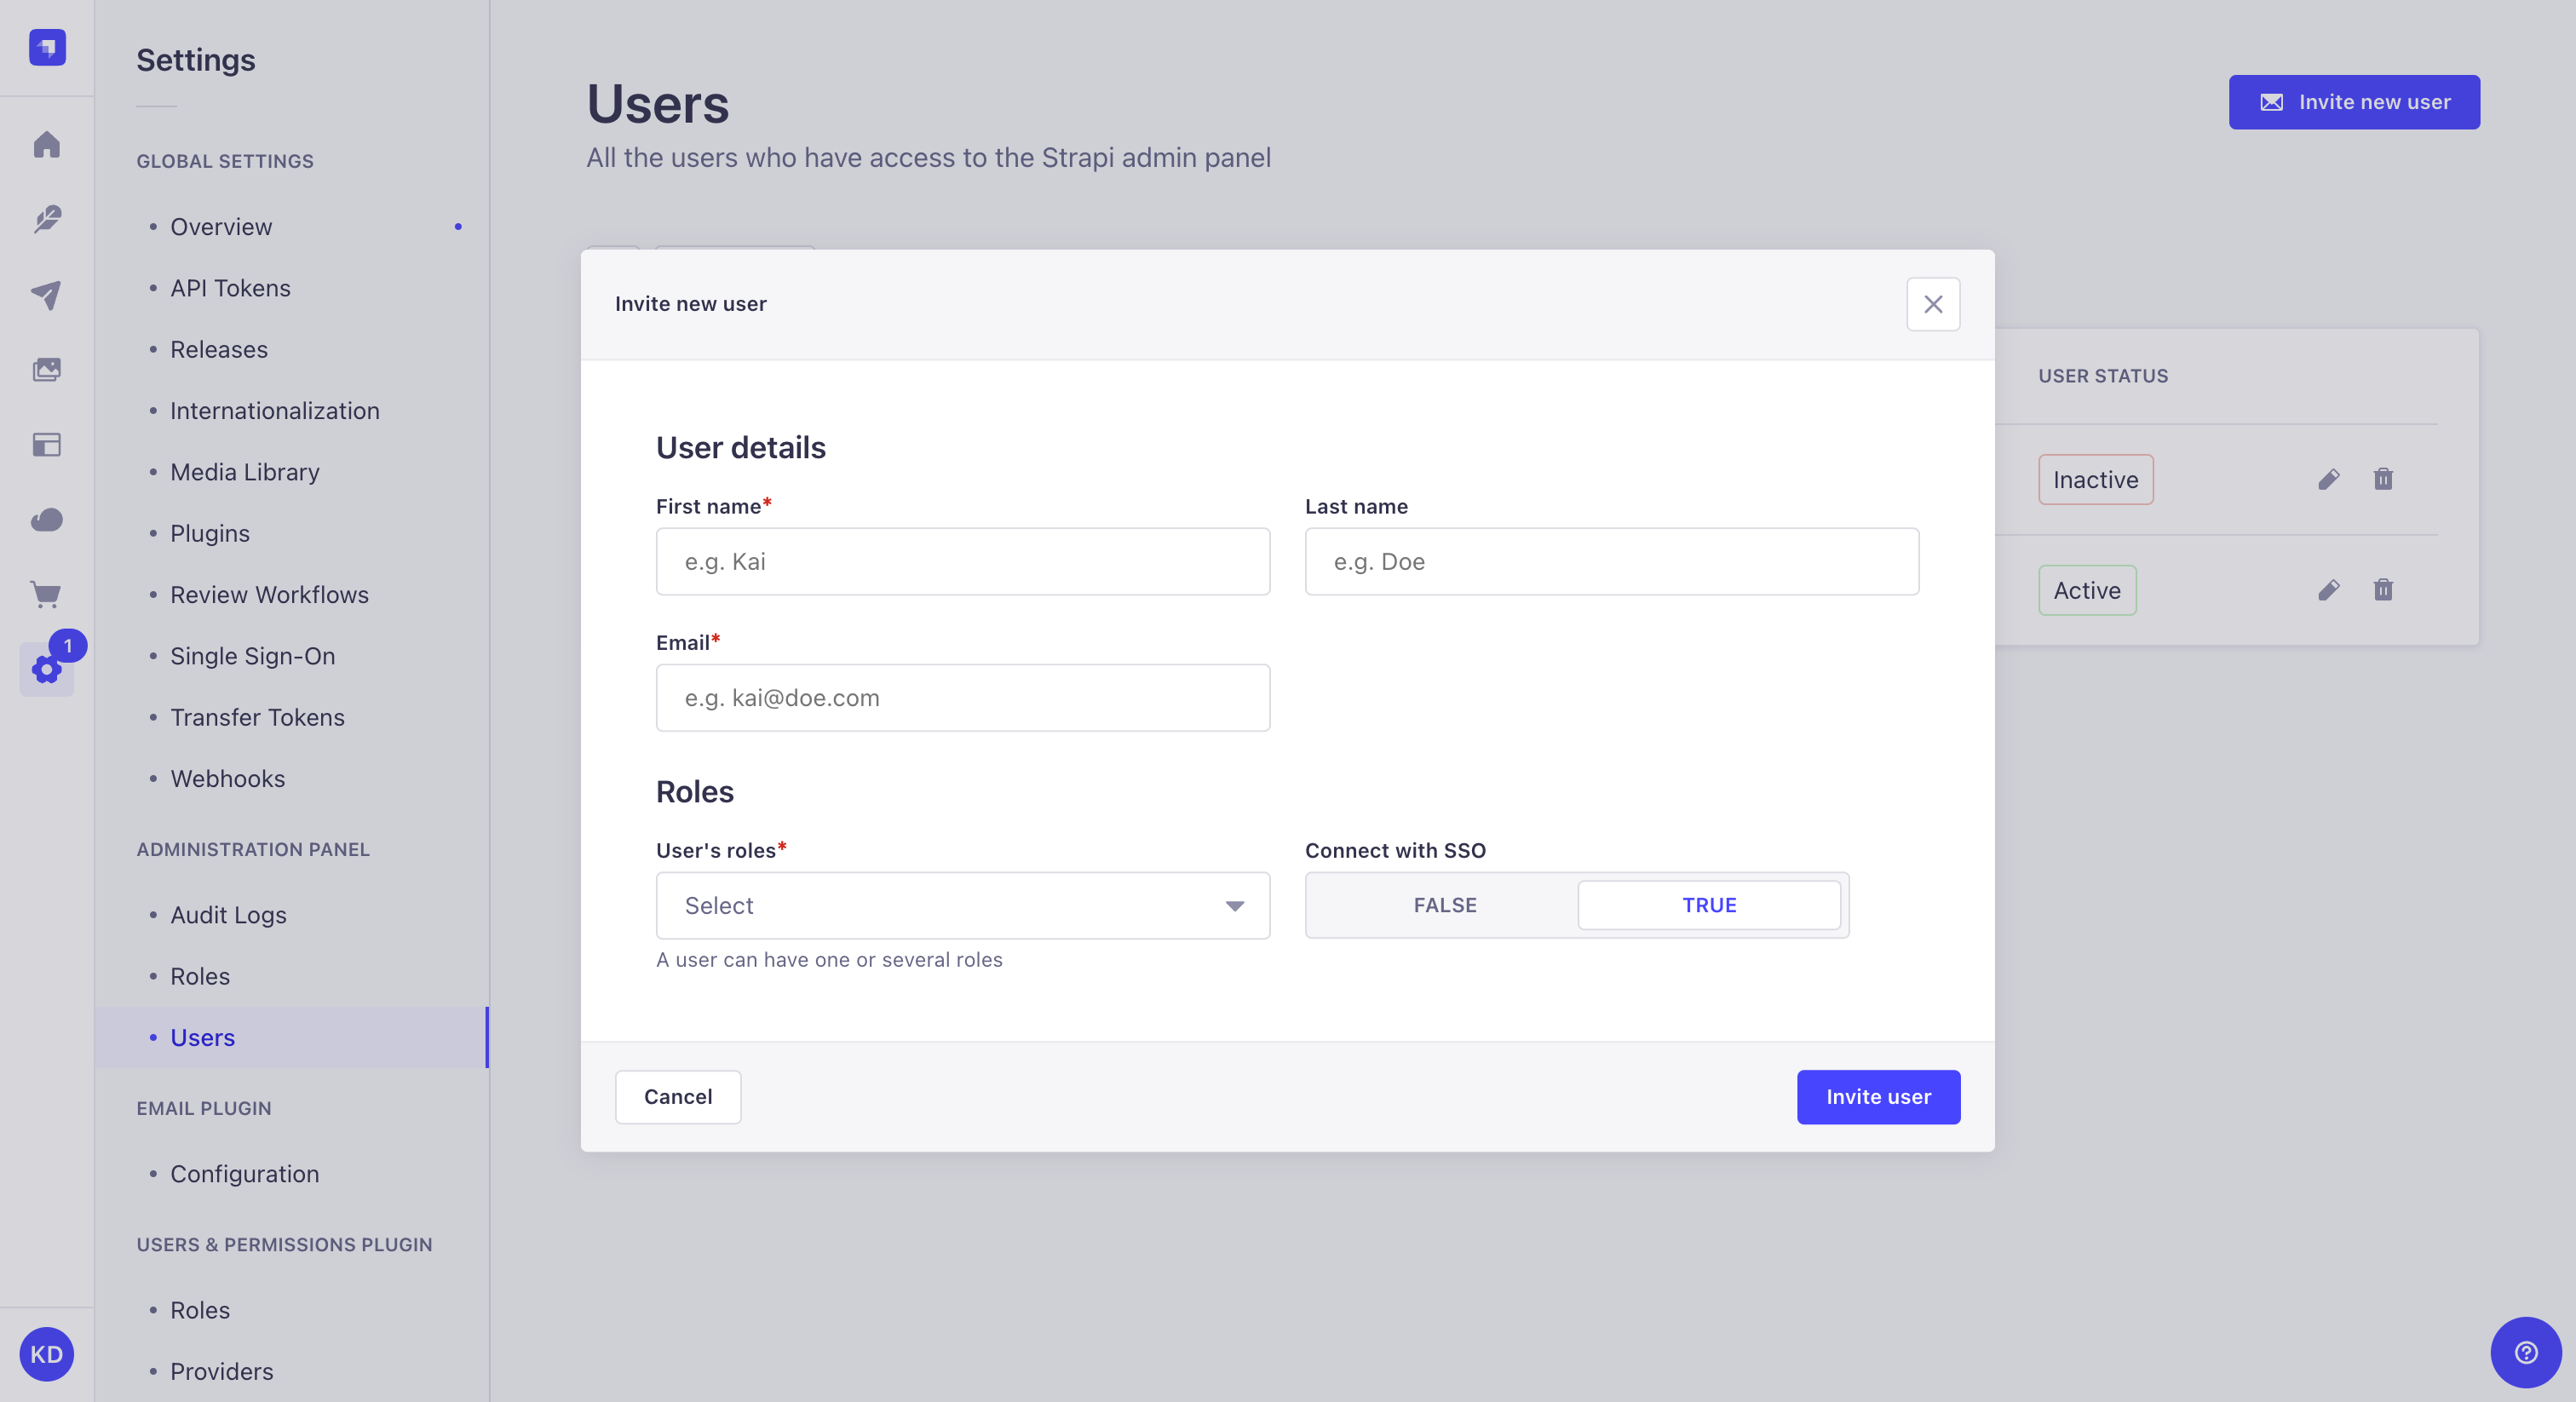
- 点击 邀请新用户按钮。
- 在邀请新用户窗口中,填写关于新管理员的详细信息:
| 用户信息 | 说明 |
|---|---|
| 名字 | (必填)在文本框中填写管理员的名字。 |
| 姓氏 | (必填)在文本框中填写管理员的姓氏。 |
| 电子邮件 | (必填)在文本框中填写管理员的完整电子邮件地址。 |
- 填写新管理员的登录设置:
| 设置 | 说明 |
|---|---|
| 用户角色 | (必填)从下拉列表中选择要分配给新管理员的角色。 |
| 连接 SSO | (可选)点击 TRUE 或 FALSE 将新管理员账户与 SSO 连接。 |
- 在 添加新用户 窗口的右下角点击 邀请用户 按钮。
- 窗口顶部会显示一个 URL:这是发送给新管理员以便他们首次登录你的 Strapi 应用的 URL。点击复制按钮 以复制该 URL。
- 点击右下角的 完成 按钮以完成新管理员账户的创建。新管理员现在应该会出现在表格中。
管理员邀请 URL 可从管理员账户访问,直至激活。
🌐 The administrator invitation URL is accessible from the administrator's account until it has been activated.
删除账户
🌐 Deleting an account
可以同时删除一个或多个管理员账户。
🌐 It is possible to delete one or several administrator accounts at the same time.
- 点击账户记录右侧的删除按钮 ,或通过勾选账户记录左侧的框选择一个或多个账户,然后点击表格上方的 删除按钮。
- 在删除窗口中,点击 确认 按钮以确认删除。
编辑账户
🌐 Editing an account
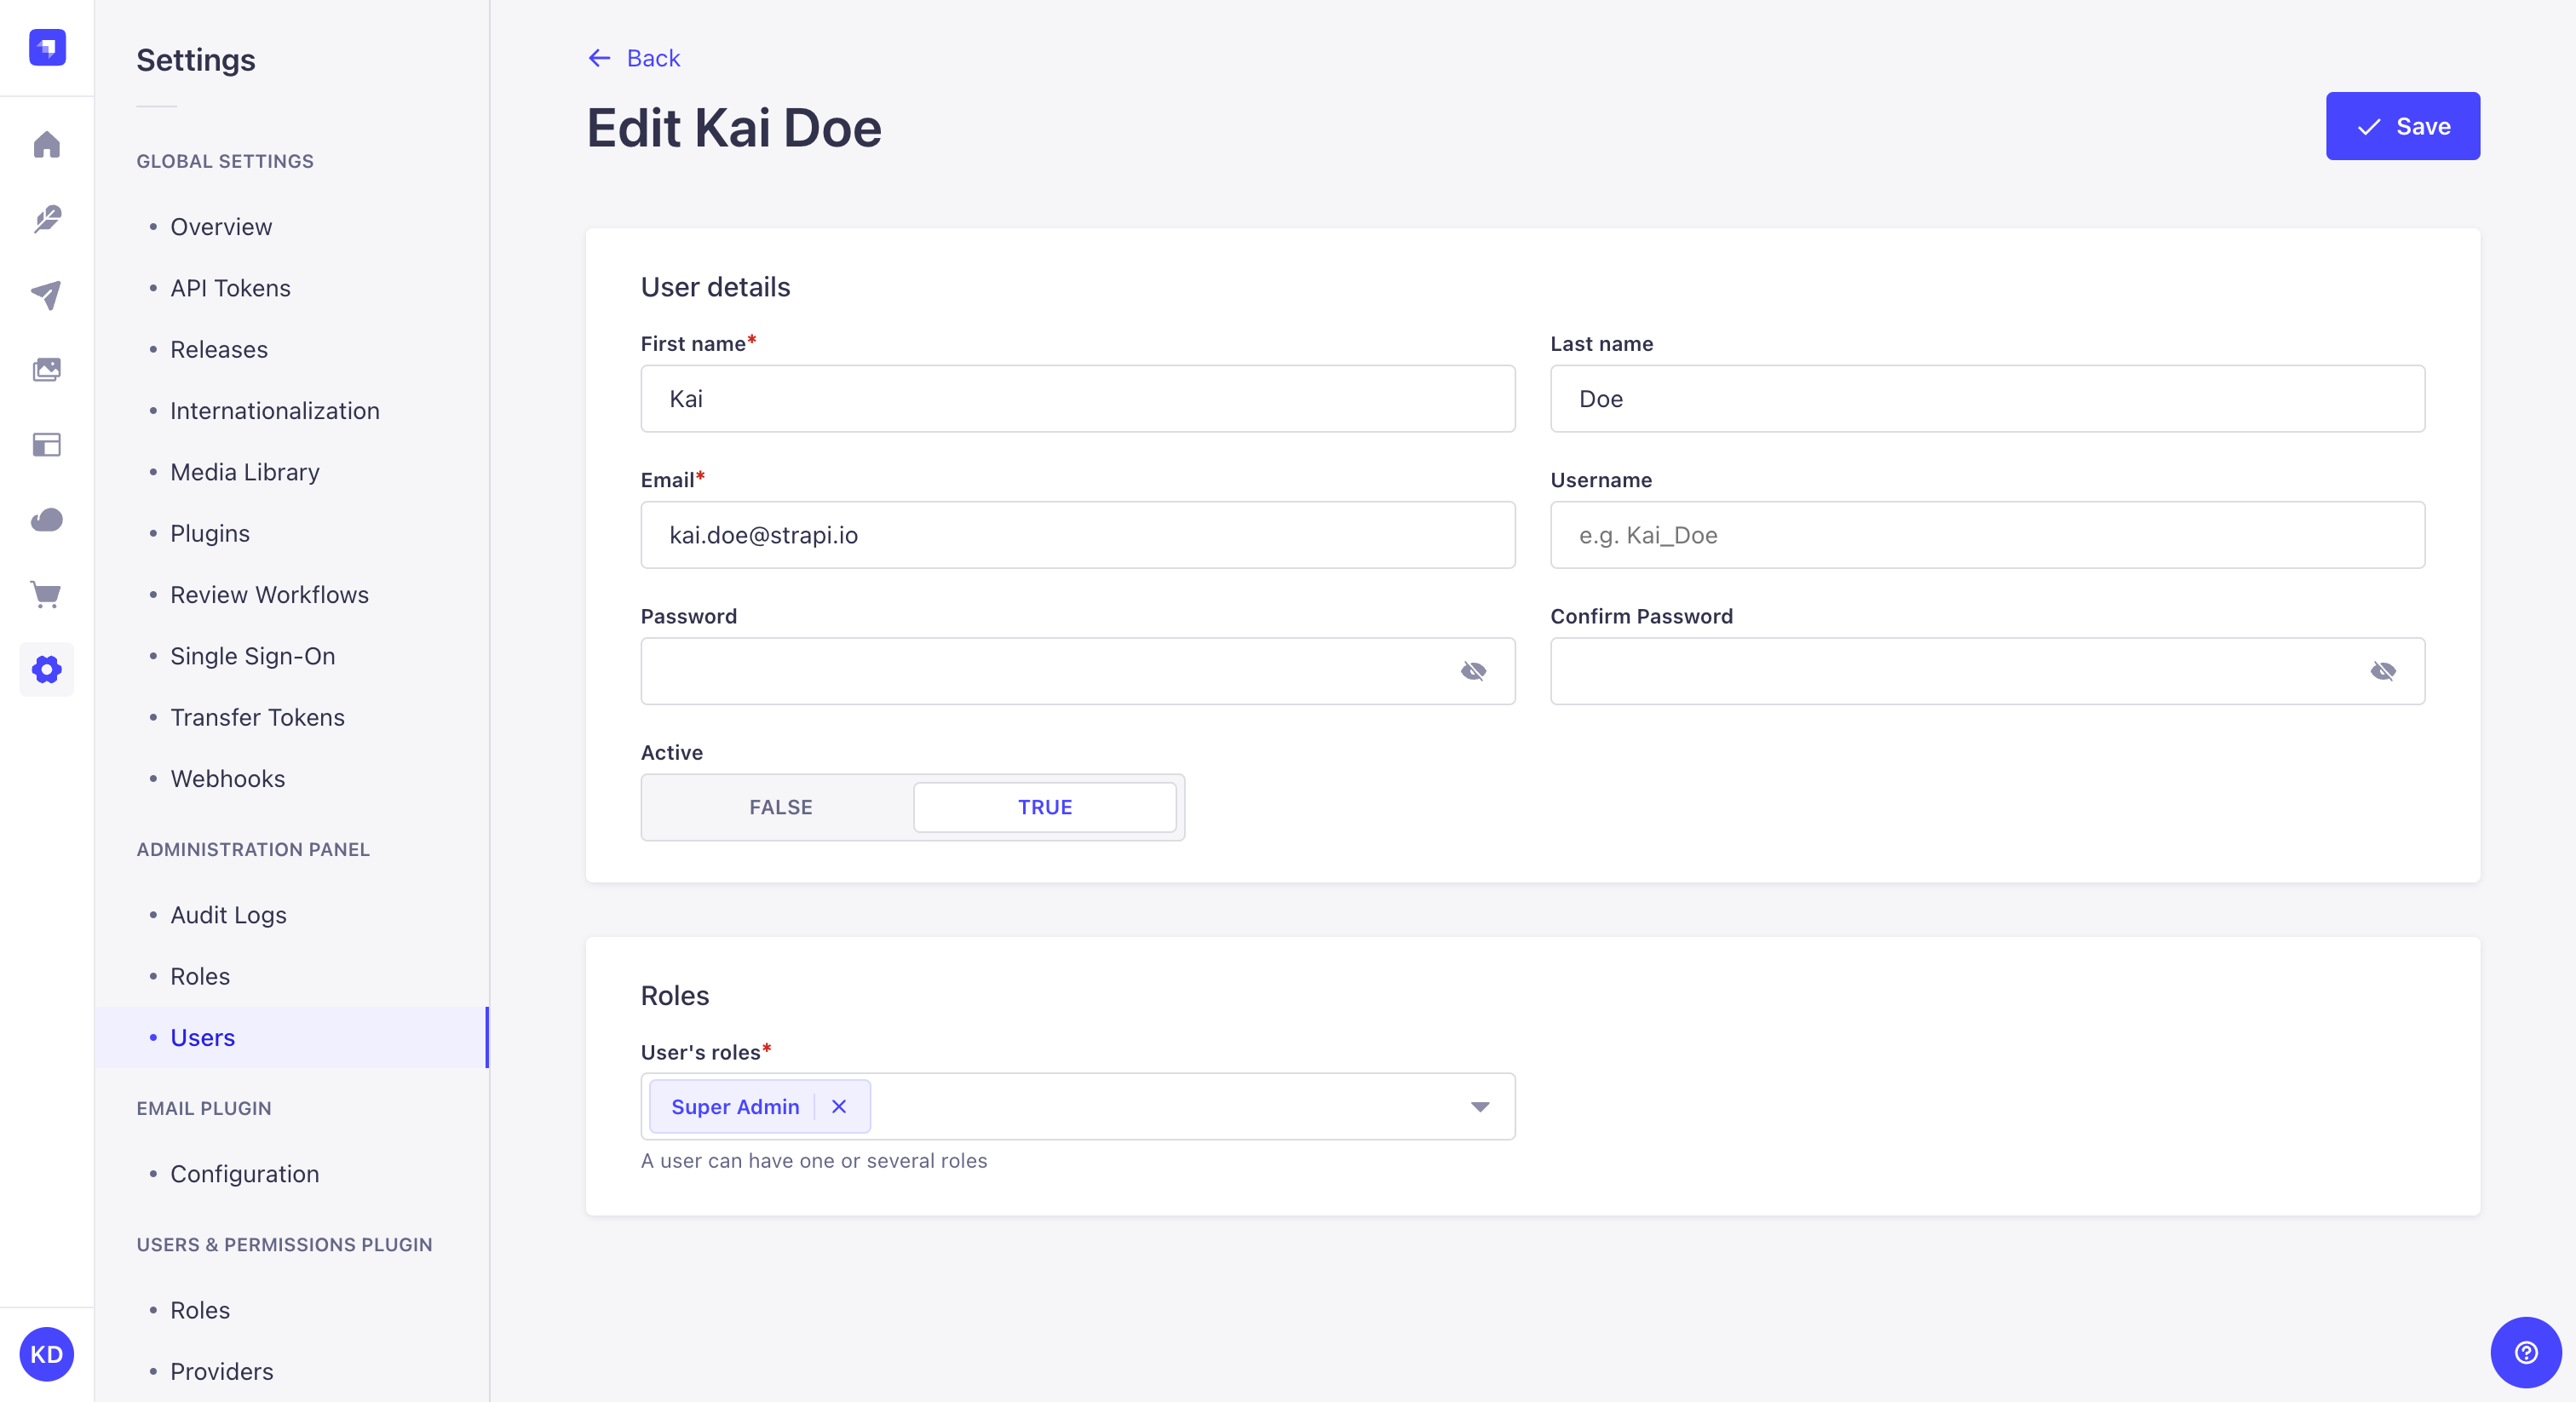
- 单击要编辑其账户的管理员的名称。
- 在详细信息区域,编辑你选择的账户详细信息:
| 用户信息 | 操作说明 |
|---|---|
| 名字 | 在文本框中输入管理员的名字。 |
| 姓氏 | 在文本框中输入管理员的姓氏。 |
| 电子邮件 | 在文本框中输入管理员的完整电子邮件地址。 |
| 用户名 | 在文本框中输入管理员的用户名。 |
| 密码 | 在文本框中输入新管理员账户的密码。 |
| 确认密码 | 在文本框中再次输入新密码以确认。 |
| 激活 | 点击 TRUE 以激活管理员账户。 |
- (可选) 在角色区域,编辑管理员的角色:
- 单击下拉列表选择一个新角色,和/或将其添加到已归属的角色中。
- 点击删除按钮 以删除已分配的角色。
- 点击右上角的保存按钮。